07:02AM - 04.08.'15
|
News Source: Wired, The Financial Time - sub. req. autoblog.com
|
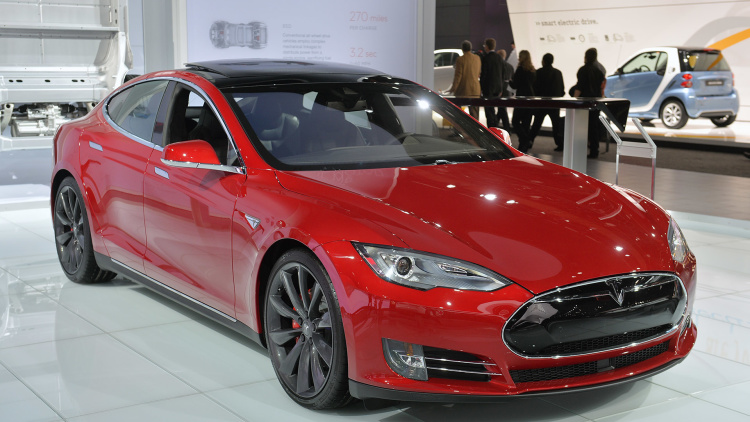
In the latest report of car hacking, security researchers were able to take control of a Tesla Model S and were able to turn off the sedan while it was driving. Unlike the recent vulnerability in FCA's Uconnect infotainment system, the exploit first required physical access to the electric sedan via an Ethernet cable. According to Wired, they then installed a trojan that granted remote access to the vehicle. "We shut the car down when it was driving initially at a low speed of five miles per hour. All the screens go black, the music turns off and the handbrake comes on, lurching it to a stop," Marc Rogers, one of the security researchers, said to the Financial Times. At higher speeds the handbrake didn't come on when the system shut off. Instead, the Model S went into neutral with the driver still having control. According to Wired, the airbags were also still fully functional. The researchers will detail six newly discovered vulnerabilities during the upcoming Def Con conference in Las Vegas. Tesla drivers have no need to fear in the meantime. The hackers worked with the EV maker to understand the holes. A Tesla spokesperson confirmed to Autoblog that the patch has already been sent over the air to the sedans. A full statement from the automaker can be read below. Tesla has had a fairly open relationship with hackers in the past. In 2014, the company offered $10,000 to any group that could gain access to a Model S. University students from China successfully won the money. Some of the company's online accounts were also once briefly hacked. |